Auth & Authorization Testing
Validate login, tokens, roles, and permission boundaries across endpoints.
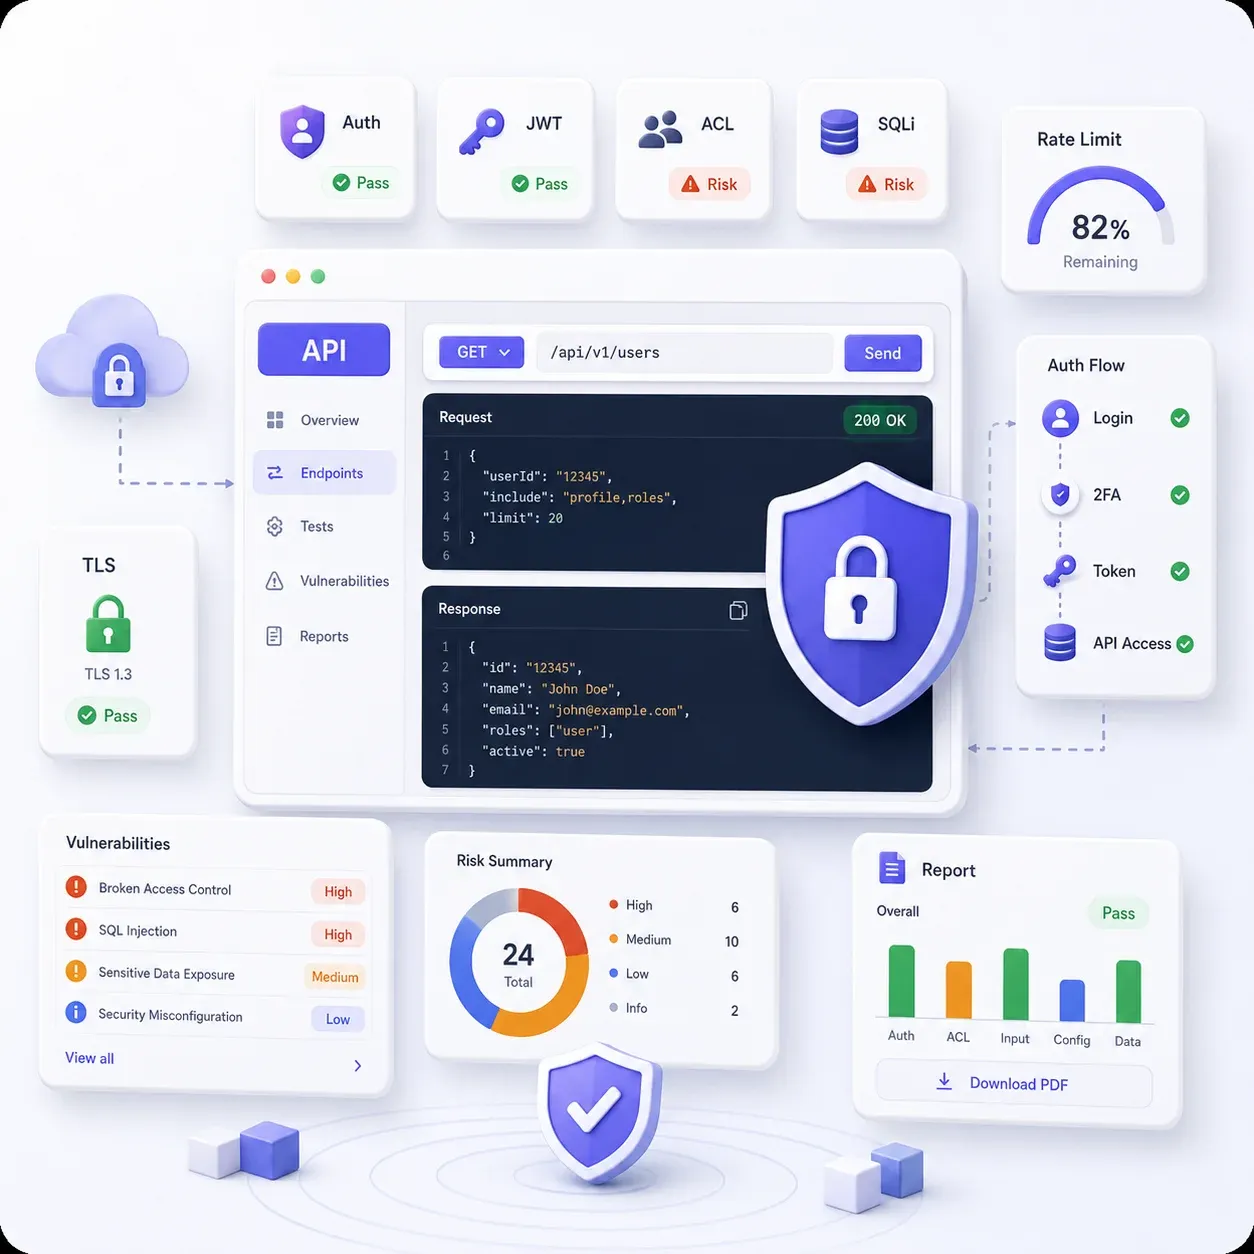
echoBitz tests your APIs for auth flaws, injection risks, and misconfigurations. Our AI-assisted scanning plus manual review finds what attackers would find first. You get clear vulnerability reports your team can act on immediately.
From authentication flows to OWASP API Top 10 checks we help you find and fix the vulnerabilities that matter.
Validate login, tokens, roles, and permission boundaries across endpoints.
Structured checks against common API security risks and misuse patterns.
Probe for injection, malformed payloads, and unsafe input handling.
Assess token lifetime, storage assumptions, and session misuse risks.
Verify throttling, brute-force protections, and abuse resistance.
Clear findings with severity, reproduction steps, and remediation guidance.
A clear API security workflow that moves from asset mapping to actionable remediation.
Map APIs, auth model, and sensitive data flows.
Define threat focus and test scope.
Execute auth, access, injection, and abuse checks.
Document vulnerabilities with severity and evidence.
Verify fixes and update residual risk notes.
We combine API clients, scanners, and manual expertise for credible findings.
We prioritize the controls that protect identity, data, and business operations.
Validate identity flows and credential handling.
Check unauthorized access to other users’ resources.
Probe unsafe input handling and query abuse.
Find insecure defaults, verbose errors, and exposure risks.
Verify abuse controls under repeated and automated requests.
Actionable findings with severity and fix guidance.
“API security is only useful when findings are clear, ranked, and reproducible.”
Endpoints, auth flows, and sensitive data touchpoints.
Scoped checks aligned to OWASP API risks.
Findings with severity, evidence, and impact.
Clear steps engineers can use to recreate issues.
Practical fix recommendations for each finding.
Verification of fixes and remaining residual risk.
echoBitz combines AI-assisted scanning with hands-on security expertise. Every finding is reproducible, prioritized, and tied to real API risk.
We focus on the vulnerabilities that expose data and break trust then give your team clear steps to fix them.
Deep checks on tokens, roles, and permission boundaries.
Structured testing against common API Top 10 risks.
Evidence and steps that speed engineering remediation.
Verify fixes before release and reduce residual risk.
Have questions about API security scope, OWASP coverage, timelines, or retesting? Here are answers to common questions about API security projects with echoBitz.
Start an API Security ProjectWe typically cover authentication, authorization, injection, misconfiguration, token security, rate limiting, and vulnerability reporting aligned to your API surface.
Yes. We use OWASP API Top 10 as a core risk framework and tailor checks to your endpoints and auth model.
A focused API set may take one to a few weeks depending on endpoint count, auth complexity, and environments. We scope after discovery.
Yes. Each finding includes severity, evidence, reproduction steps, and practical remediation guidance.
Yes. Retesting is part of a complete engagement so you can confirm fixes before release.
Contact echoBitz for a free consultation. We review your APIs, auth model, and risk priorities, then propose a tailored security testing plan.