Over-Provisioned Access
Permissions granted for one task never get revoked, so users accumulate rights far beyond their role.
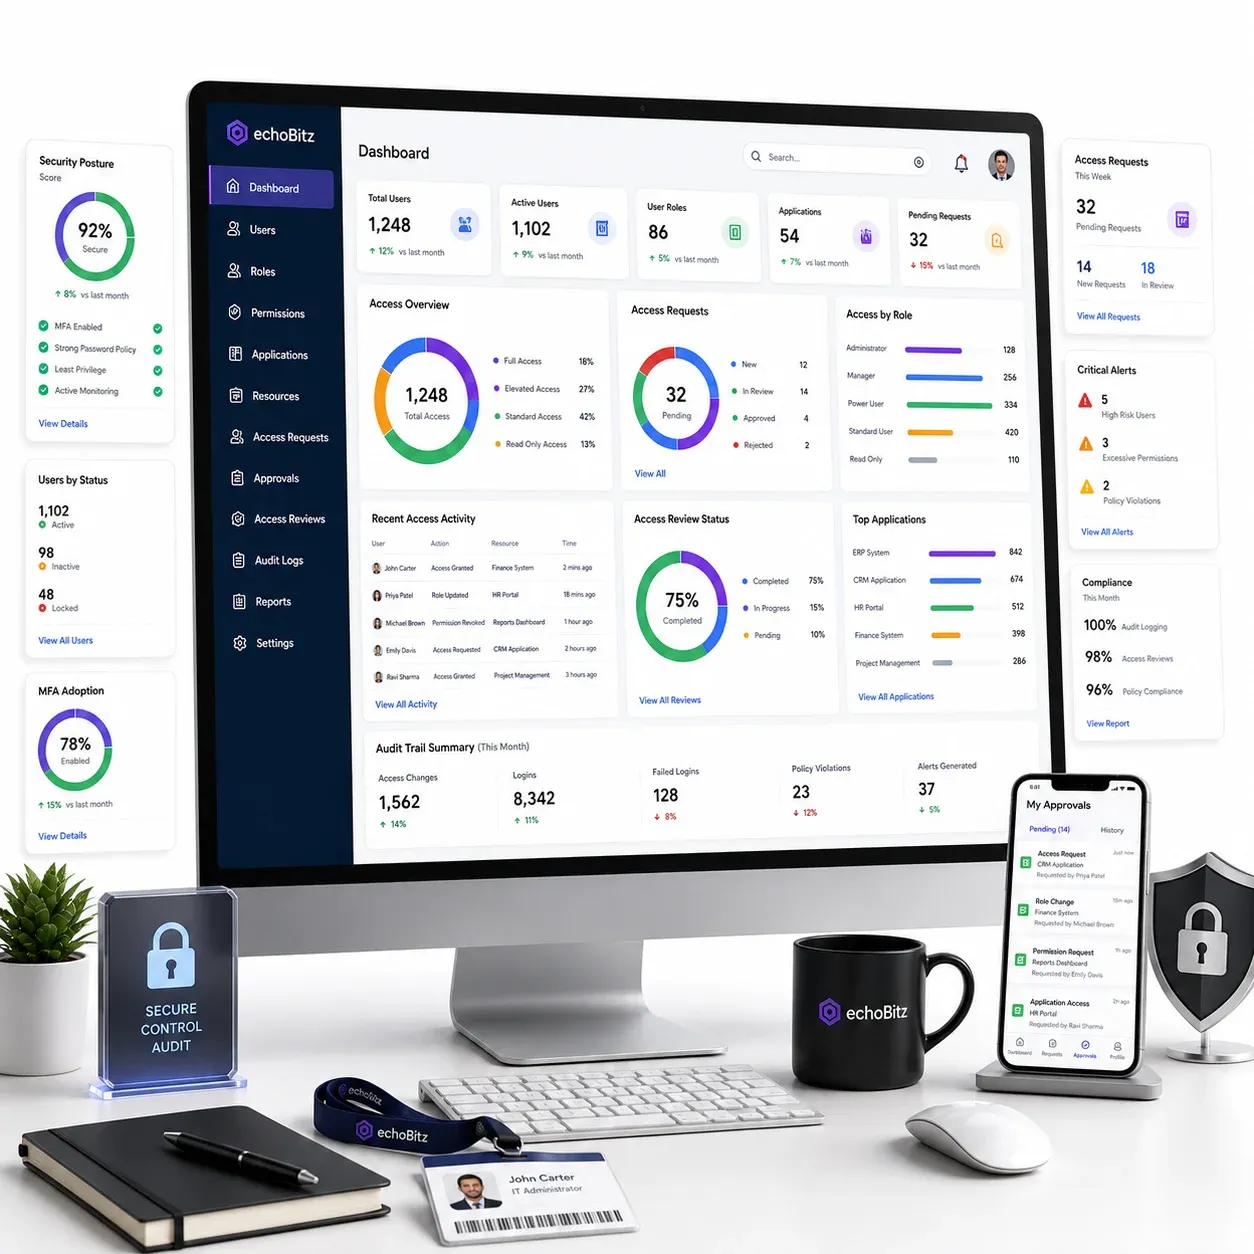
Privilege Creep RiskWhat if every role, permission, approval, and access change lived in one auditable system? echoBitz delivers access management with AI-driven anomaly detection for organizations that need least-privilege control and clean audit trails.
Ad-hoc permissions, shared logins, and untracked access changes create audit gaps and quietly expand who can touch sensitive data.
Permissions granted for one task never get revoked, so users accumulate rights far beyond their role.
Privilege Creep RiskAccess requests handled over chat or email skip proper review and leave no record.
Governance RiskWhen one person can both request and approve, fraud and error controls break down.
Compliance RiskWithout a log of who changed what and when, audits stall and incidents are hard to investigate.
Audit Failure RiskModernize access control with an integrated system that connects roles, permissions, approvals, segregation of duties, and audit trails in one Odoo flow.
Access Rules Managed
10,000+ Active ControlsAudit Prep
−50% vs. Manual ReviewsAccess Reviews
Automated Periodic recertification rulesAccess Insights
Live Analytics Role-based dashboard accessA connected access stack for roles, permissions, approvals, segregation of duties, audit trails, and SSO-ready control.
Define role-based access with least-privilege defaults.
Benefit: Reduced Attack SurfaceRoute access requests to the right approvers with records.
Benefit: Governed Access GrantsPrevent conflicting rights that undermine controls.
Benefit: Stronger Fraud PreventionImmutable logs of every access change and approval.
Benefit: Audit-Ready EvidencePeriodic reviews confirm access is still appropriate.
Benefit: Less Privilege CreepIntegrate with identity providers for centralized sign-on.
Benefit: Simpler, Safer LoginMove from ad-hoc permissions and shared logins to a unified access ecosystem designed for least privilege, clean approvals, and defensible audits.
Spreadsheet permission lists, email approvals, and shared credentials defined the traditional access model.
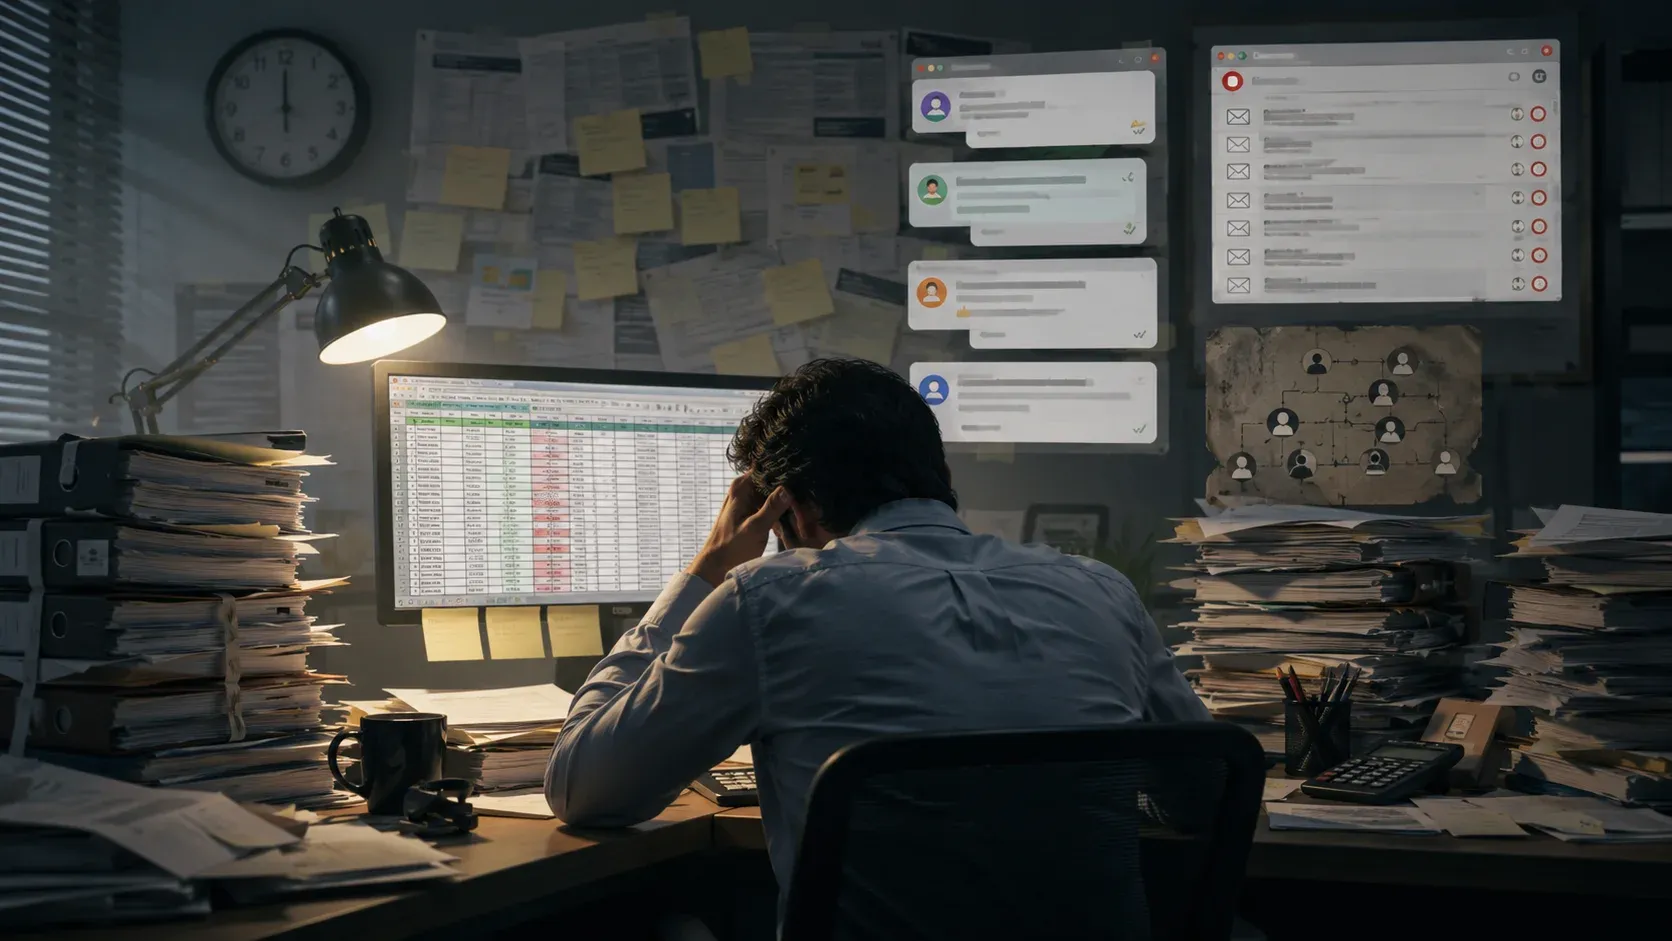
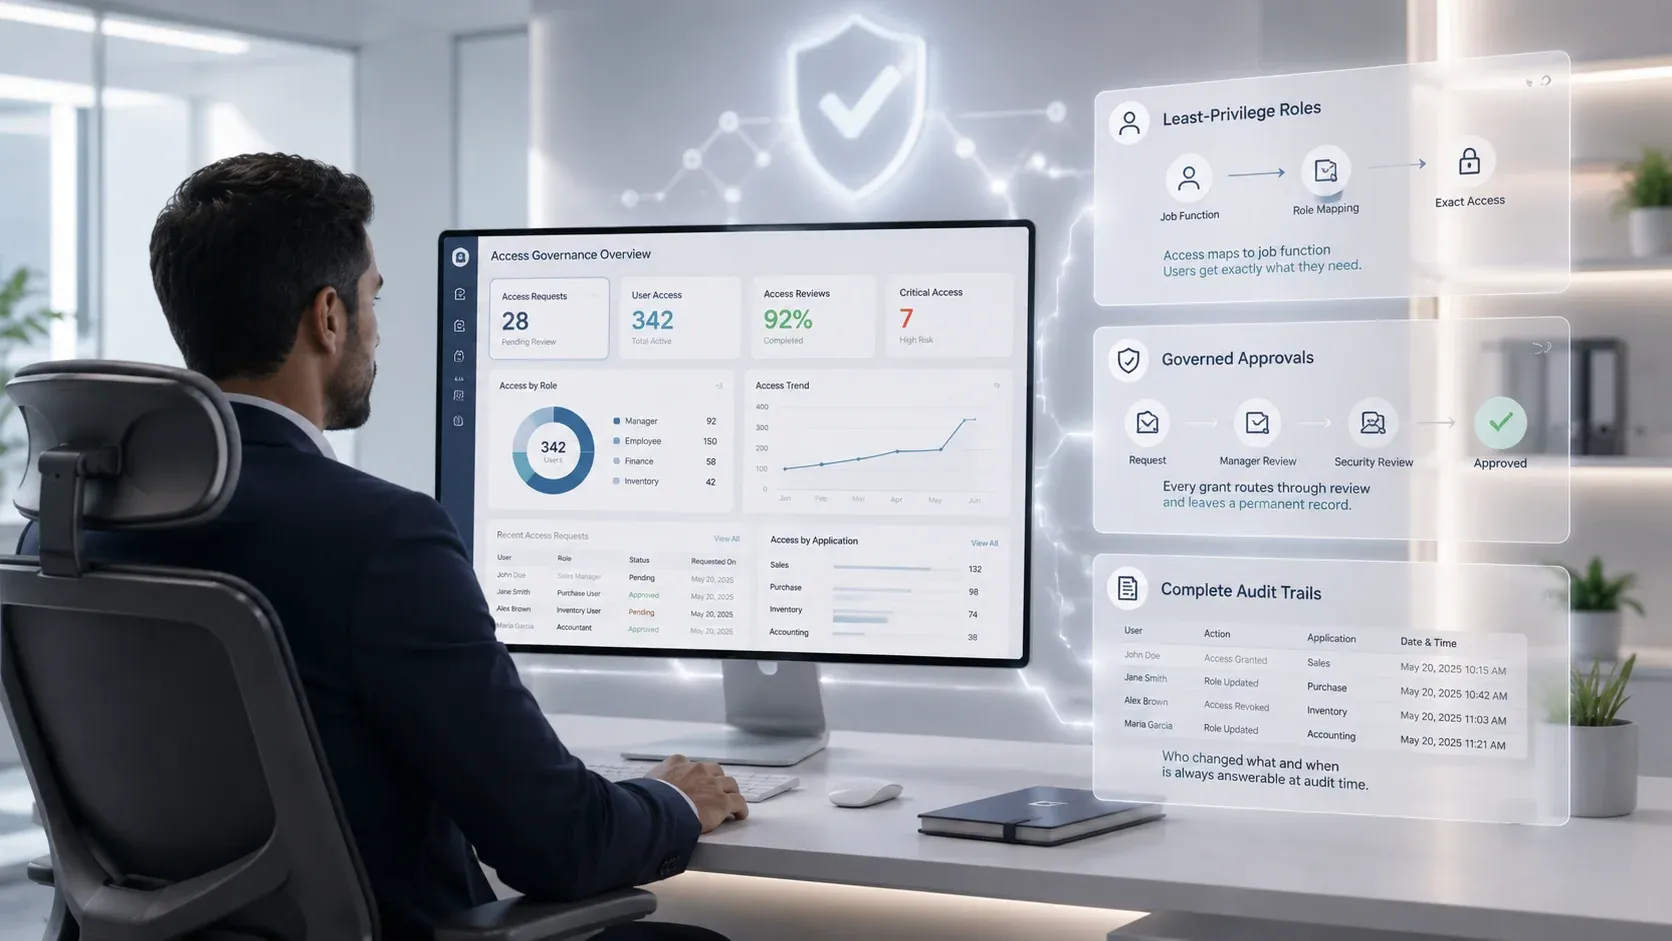
Transitioning to access-first Odoo meant control at every step from request to approval to recertification.
Govern access the way security and compliance demand. From role design and approval routing to segregation of duties and audit trails, we configure Odoo to enforce least privilege across your organization.
See who has access to what, by role, system, and approval history.
Native Odoo links to HR and identity providers for a single access truth.
Support from specialists who understand IT, security, and audit pressure.
echoBitz bridges identity and operations so roles, permissions, approvals, and audit data stay aligned across systems.
Least-privilege role design across modules and systems.
Structured access requests with reviewers and records.
Complete logs of access changes for defensible audits.
Integrate with identity providers for centralized sign-on.
Rules prevent conflicting rights that break controls.
Joiner-mover-leaver events keep access current with roles.
Have questions about roles, permissions, approvals, segregation of duties, audit trails, or Odoo access setup? Here is what IT and compliance teams usually ask before starting.
Talk to an Access ExpertIt is an Odoo-based solution for roles, permissions, approval workflows, segregation of duties, audit trails, and SSO-ready control in one governed workflow.
Yes. Role-based permissions ensure users get exactly the access their job requires, and recertification reviews remove excess rights over time.
Yes. Access requests route to the right approvers and leave a permanent record, so grants are governed and traceable.
Yes. Rules prevent conflicting rights such as request and approval by the same person to strengthen fraud and error controls.
Yes. It can integrate with identity providers for centralized single sign-on and consistent access policies.
A focused rollout can start after discovery. Custom role design, approval routing, and identity integration may need additional sprints.